Mohammed Samir web security

Currently: HTB Web PT path — SQLMap Essentials

$ whoami

who ami_

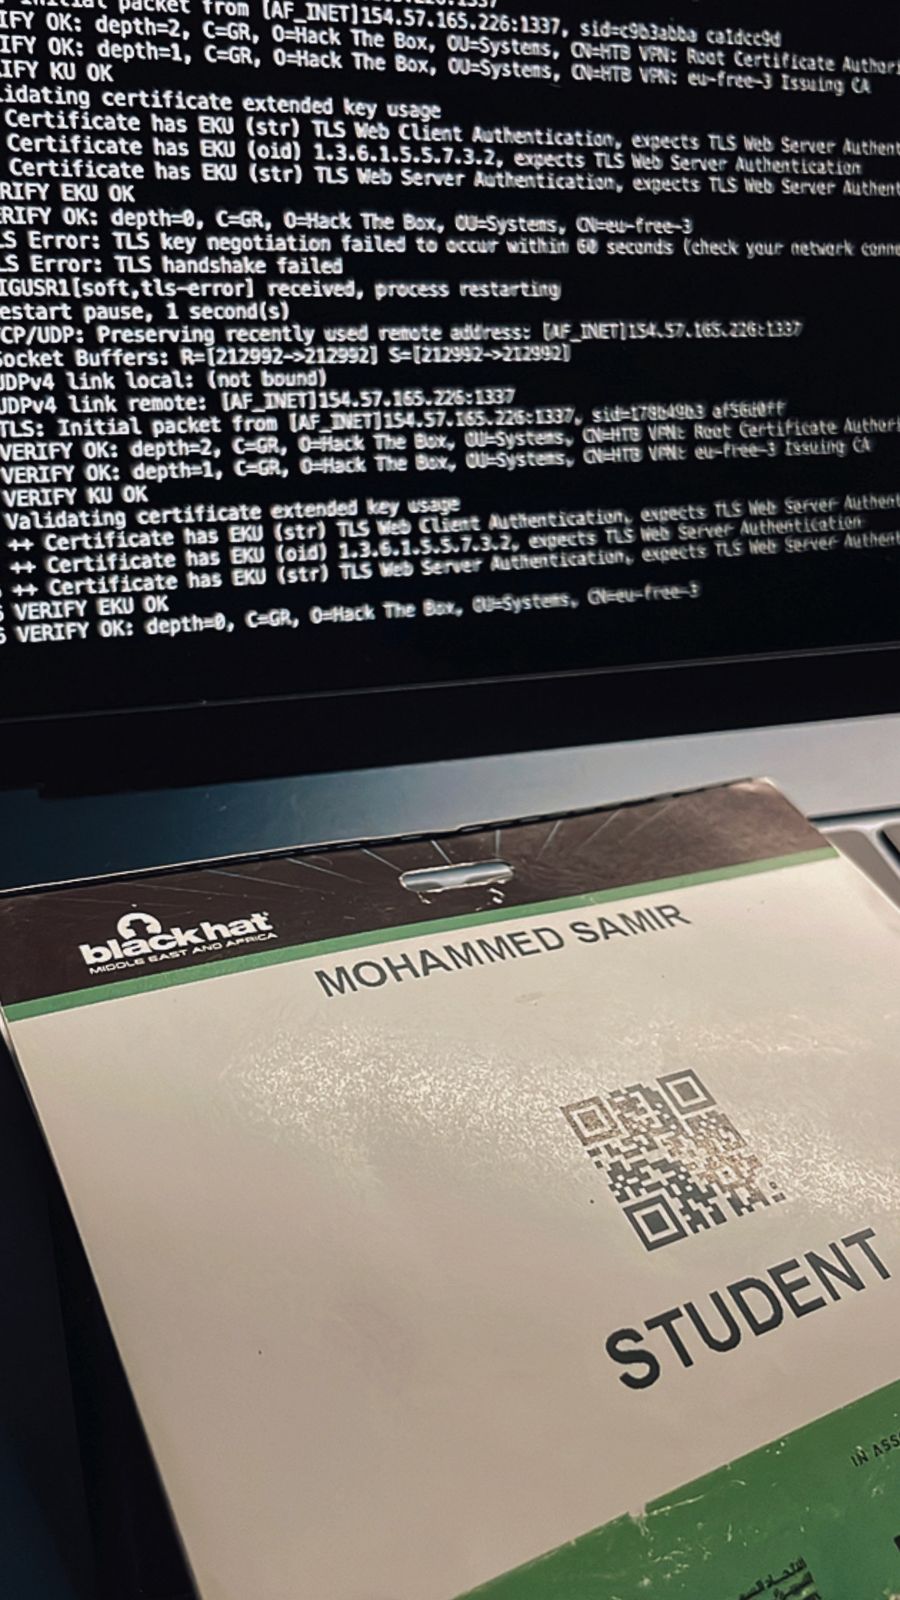
Black Hat MEA 2024 attendee badge — Mohammed Samir
black hat mea 2024 — attended

I'm Mohammed Samir, aka 0xMYTH. First-year Cybersecurity student and OffSec enthusiast — web exploitation, CTFs, and building autonomous agents that hunt flags.

handle
0xMYTH
currently
HTB Web PT path — SQLMap Essentials
attended
Black Hat MEA 2024
certified
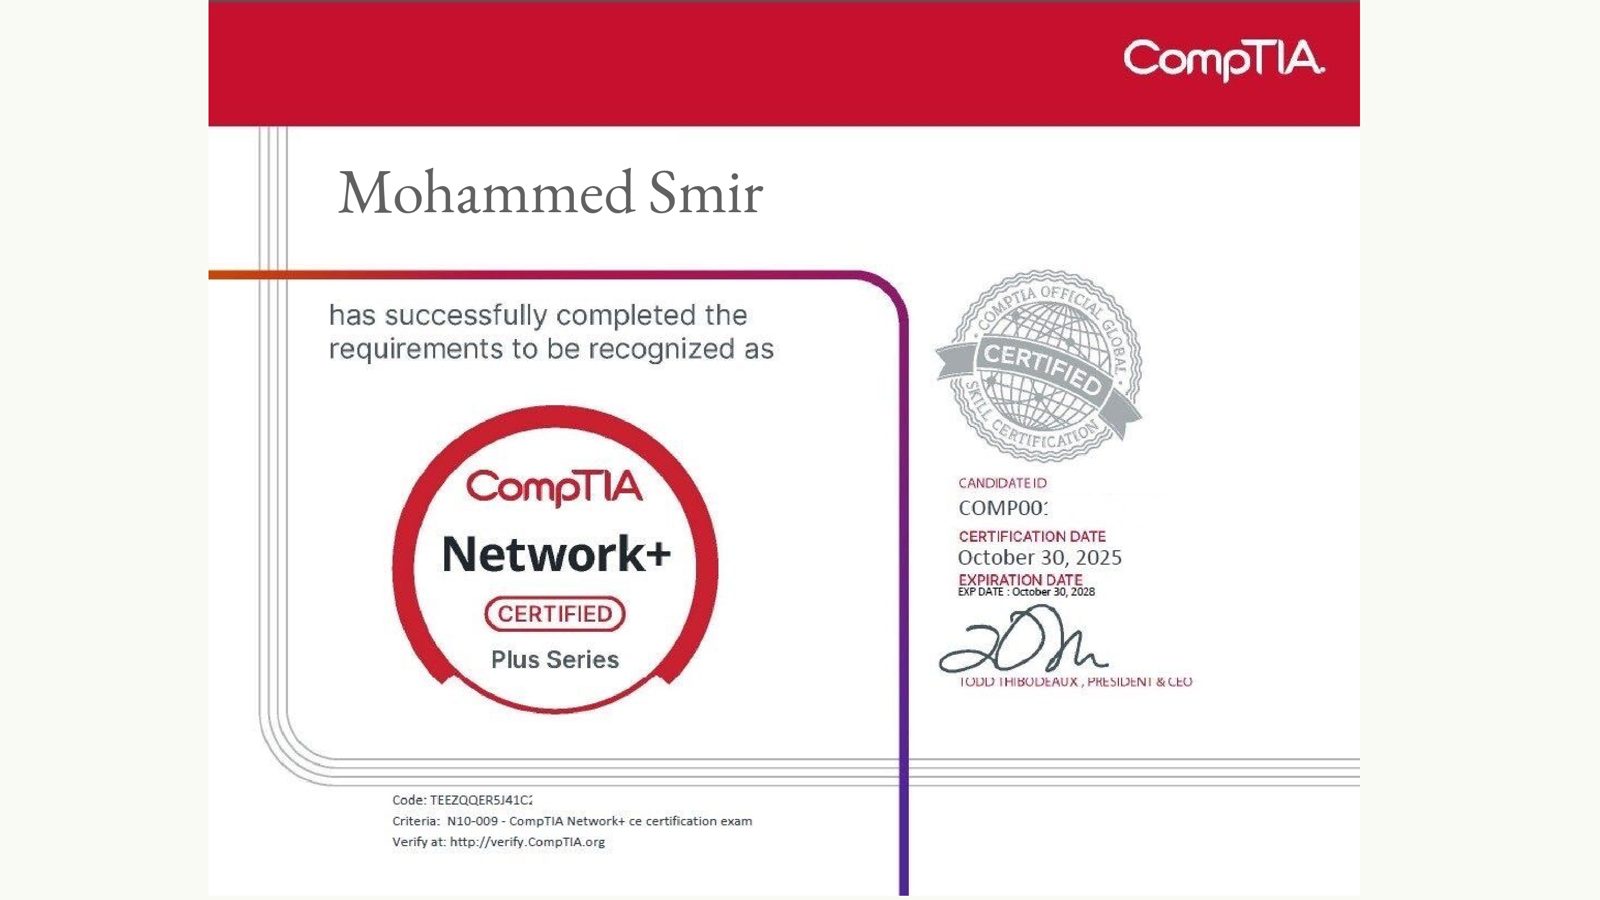
CompTIA Network+
goal
path completion by October 2026 · top 100 at Black Hat MEA
the stack
  • Focus: Web Exploitation, CTFs, AI Agents, Python, Linux, Docker
  • Tools in rotation: ffuf, feroxbuster, gobuster, wfuzz, Burp Suite, sqlmap, nuclei, nikto
  • Infrastructure: fedora, nginx, gunicorn, systemd, cloudflare
  • Built with: flask, postgres (supabase), sqlite, leaflet.js / openstreetmap, pi (node/typescript), claude + openai apis, openrouter, docker

## now

current focuslive

HTB Web Penetration Tester path

8/ 9 modules

  1. [✓]01Web Fuzzing
  2. [✓]02JavaScript Deobfuscation
  3. [✓]03Cross-Site Scripting (XSS)
  4. [✓]04SQL Injection Fundamentals
  5. [▸]05SQLMap Essentials — in progress
  6. [✓]06Web Requests
  7. [✓]07Introduction to Web Applications
  8. [✓]08Web Proxies
  9. [✓]09Information Gathering — Web Edition

tools in rotation: ffuf · feroxbuster · gobuster · wfuzz · Burp Suite · sqlmap · nuclei · nikto

→ path completion by October 2026 · top 100 at Black Hat MEA

## projects

$ systemctl status 0xmyth-*

ctf-agent.service

active (in development)

Autonomous CTF Exploitation Agent

Loaded:
pi (node/typescript) · docker · claude + openai apis · openrouter
Repo:
url pending — releasing after competition

An autonomous agent that solves web-exploitation and binary-exploitation (pwn) CTF challenges during live competition — no human in the loop on the day. Built on the Pi coding-agent framework; the real engineering is a hand-authored AGENTS.md instruction set: authorization framing, an evidence-gated methodology where every claim is either confirmed or a guess, and pivot-on-failure logic to stop the model brute-forcing a dead approach — backed by a pruned CTF skills stack, a Docker sandbox that runs x86-64 pwn on Apple Silicon, and a dead-simple checkpoint file that survives a crash or restart.
  • ai agents
  • pi framework
  • llm tool-calling
  • web exploitation
  • pwn
  • docker

car-rental.service

active (live prototype)

Car Rental Management System

Loaded:
flask · postgres (supabase) · hijri-converter

Rebuilt from a single-file HTML prototype into a full Flask application for a family car-rental business. Arabic RTL layout, printable legal contracts with Hijri date support, and e-signature capture. Started on SQLite; migrated to Supabase Postgres for hosted deployment.

  • flask
  • postgres
  • arabic rtl
  • hijri dates
  • e-signature

tafweej.service

active (production)

Tafweej Workforce Management System

Loaded:
flask · sqlite · leaflet.js / openstreetmap
Client:
Al-Elyani Company — Hajj season operations

Replaced 30+ disconnected Excel files used through Hajj season with one system: employee management, daily deployment, fleet tracking for 40+ buses, equipment custody with audit trails, Tafweej movement scheduling, a live operations map with Ministry-approved routes, and Excel export.

  • flask
  • sqlite
  • leaflet.js
  • audit trails
  • excel export

0xmyth-web.service

active (running)

This site's infrastructure

Loaded:
fedora · nginx · gunicorn · systemd · cloudflare

Self-hosted on a box I administer: Flask apps served by Gunicorn behind Nginx on Fedora, managed as systemd units, with Cloudflare in front. Listed here to show real infrastructure ownership — not tutorial-following.

  • fedora
  • nginx
  • gunicorn
  • systemd
  • cloudflare
→ drag to browse units 01 / 04

## ctf & achievements

ucsi26 · ai-driven ctf

1st place [university]

national ctf · malaysia

3rd place [top 3 national]

bhmea-2025 qualifiers

rank 120 [needed: top 100]

## certifications

network+

CompTIA Network+ — certified

CompTIA Network+ certificate — Mohammed Samir

## writeups

~/writeups
$ ls writeups/
no entries yet — first writeup in progress

## contact

talk shop.

Open to CTF teams, security collaborations, and new opportunities — internships, freelance work, or interesting projects. Just as happy to talk shop about web exploitation, agents, and offensive security.